Attack Path Analysis Guide for Security Leaders
A critical vulnerability is not automatically a critical business risk. A flaw becomes dangerous when an attacker can reach it, exploit it, move from it, and use the resulting access to affect valuable systems or data. This attack path analysis guide explains how security leaders can evaluate that full chain instead of treating every finding as an isolated technical issue.
Attack path analysis brings operational context to vulnerability management, penetration testing, and red team results. It asks the question that matters during a real intrusion: given the access an attacker can realistically obtain, what is the shortest credible route to a business-critical objective?
What Attack Path Analysis Actually Measures
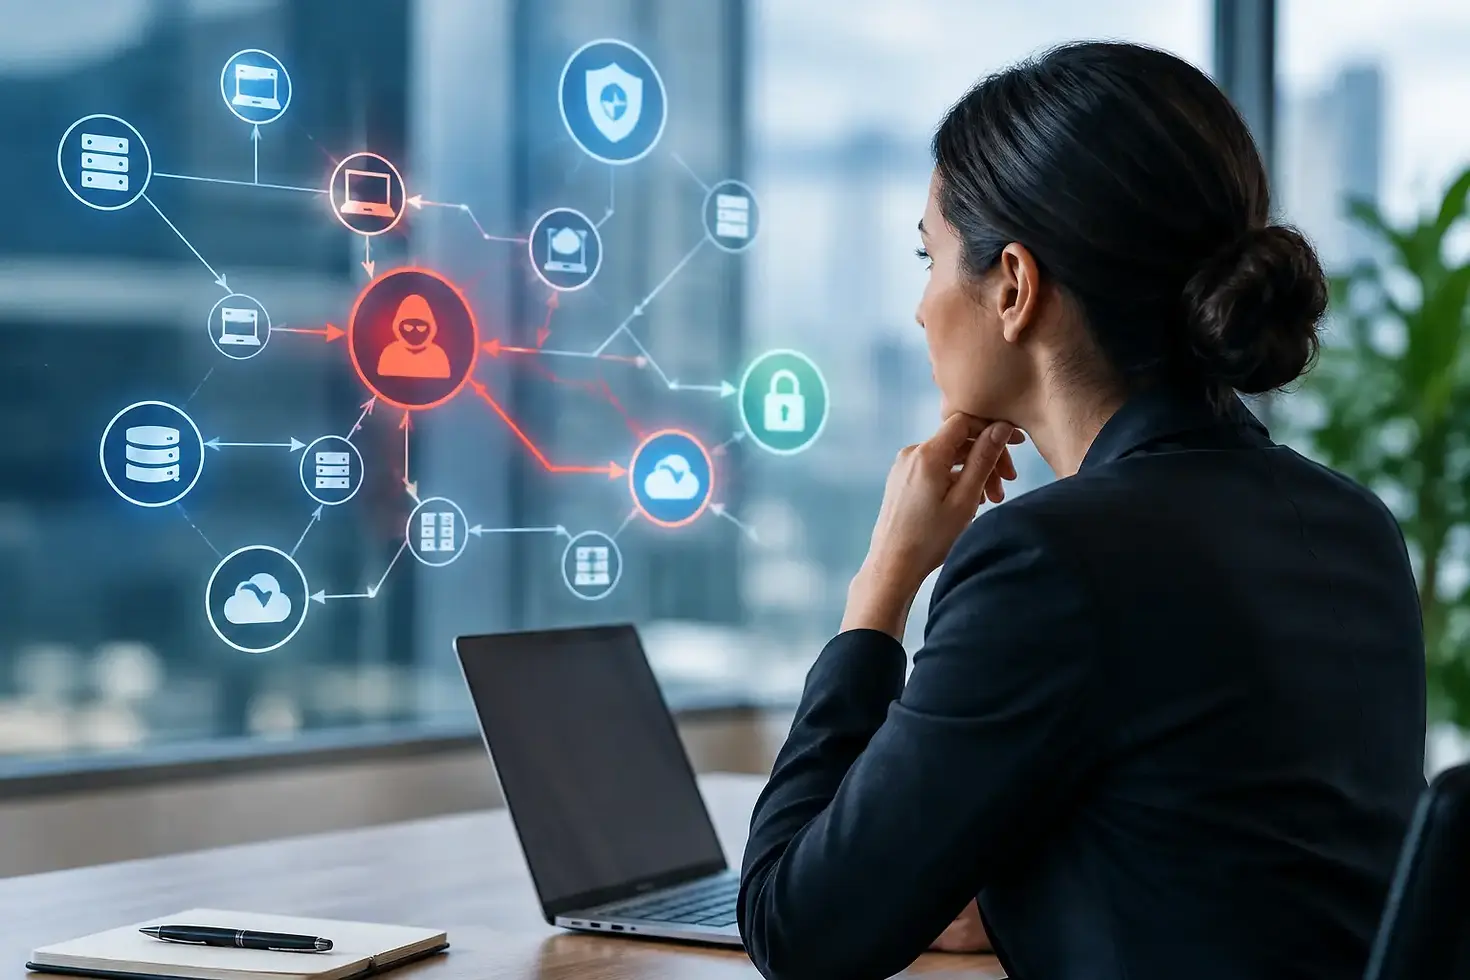
An attack path is a sequence of conditions, weaknesses, permissions, and trust relationships that could allow an attacker to progress from an initial foothold to a defined objective. That objective may be domain administrator access, cloud control plane access, sensitive customer data, payment systems, source code, or an operational technology environment.
The analysis is not limited to software vulnerabilities. It includes exposed services, weak identity controls, excessive permissions, insecure configurations, stale accounts, shared credentials, unsegmented networks, vulnerable applications, and human entry points such as phishing. A path can begin with a low-severity issue and still create high business impact if it connects to a privileged asset.
This distinction changes remediation decisions. A missing patch on an isolated internal workstation may deserve routine treatment. The same weakness on an internet-facing server that can access a privileged management network deserves immediate attention. Severity scores help classify individual flaws, but they do not prove exploitability in a specific environment.
Why Point-in-Time Findings Are Not Enough
Traditional vulnerability assessments provide essential coverage. They identify known weaknesses, missing updates, insecure settings, and outdated components at scale. However, a vulnerability list does not show how separate weaknesses interact.
Attackers do not work from a remediation spreadsheet. They test assumptions, collect credentials, identify accessible systems, abuse trusted connections, and look for routes around security controls. A red team engagement applies that adversary mindset under authorization, testing whether preventive and detective controls hold when several small weaknesses are combined.
For executives, attack path analysis translates technical findings into a more defensible risk statement. Instead of reporting that hundreds of vulnerabilities exist, security teams can explain that an external attacker could potentially compromise a user account through phishing, access a poorly segmented application environment, and reach data governed by regulatory obligations. That narrative supports faster decisions on funding, ownership, and remediation timelines.
Start With the Assets That Matter Most
Effective analysis begins with defined crown jewels. If the destination is unclear, the work can turn into broad infrastructure exploration without a business decision attached to it. Security and business stakeholders should identify the systems, data stores, identities, and processes whose compromise would create unacceptable operational, financial, legal, or reputational consequences.
For some organizations, the priority is customer data in a cloud platform. For others, it is the identity infrastructure that grants access across the enterprise, a production application, intellectual property repositories, or systems supporting regulated operations. The most valuable target is not always the most obvious one.
Then establish realistic attacker starting positions. An external unauthenticated attacker, a phishing-compromised employee, a malicious insider, and a vendor with legitimate remote access all have different opportunities. A mature program tests more than one scenario because a control that blocks internet-based exploitation may do little to prevent misuse of valid credentials.
Define Reachability and Trust
Once the starting point and objective are established, map what connects them. Review network routes, firewall rules, VPN access, application integrations, cloud identity relationships, Active Directory trusts, privileged access workflows, and service accounts. The goal is to identify whether a compromised account or host can communicate with, authenticate to, or influence the next asset in the chain.
Trust relationships deserve particular scrutiny. Attack paths frequently cross boundaries that teams assume are isolated: a development account with production permissions, a backup service account with excessive rights, a third-party integration token, or an endpoint management platform that can execute code across thousands of devices.
Validate the Path Through Ethical Hacking
A diagram of potential relationships is useful, but it is not proof. Technical controls may interrupt the route. Multifactor authentication may stop credential reuse, endpoint detection may contain malicious activity, segmentation may block lateral movement, or a privilege management control may prevent escalation.
That is why attack path analysis should be validated through authorized ethical hacking. Skilled testers safely verify whether each stage is achievable without causing business disruption. They document the evidence required to demonstrate access, the controls encountered, the methods that succeeded or failed, and the practical impact if the path were abused by a criminal actor.
Validation must be governed by clear rules of engagement. Scope, testing windows, systems excluded from exploitation, escalation contacts, data-handling requirements, and stop conditions should be agreed before work begins. High-consequence environments may require non-destructive proof rather than full objective access. The assessment should be realistic, but responsible testing is never optional.
Test Detection Alongside Prevention
A blocked attack is a positive result only if the organization can confirm why it was blocked. Attack path exercises should assess visibility at each meaningful stage: phishing delivery, suspicious authentication, privilege escalation, lateral movement, cloud permission changes, and unusual data access.
Detection coverage is not simply a matter of generating alerts. Analysts need sufficient context to determine what happened, what was affected, and whether the adversary remains active. This is where digital forensics capability strengthens offensive testing. Evidence collection, log retention, endpoint telemetry, and investigation workflows determine whether a security team can reconstruct the path under pressure.
A red team may deliberately avoid evasive techniques in one engagement to measure baseline detection, then use more realistic tradecraft in a later exercise after monitoring improvements are in place. The right approach depends on the organization’s maturity, risk tolerance, and objective for the engagement.
Prioritize Remediation by Breaking the Chain
The best remediation is not always the fix closest to the final target. It is the control that breaks the attack path most reliably, with the least operational risk and the fastest achievable implementation.
For example, patching an exposed application flaw may eliminate the initial access vector immediately. In another case, enforcing phishing-resistant multifactor authentication could prevent account takeover across several potential paths. Removing excessive privileges from a service account may block escalation to critical systems even if an endpoint remains vulnerable.
Security leaders should weigh exploitability, business impact, control coverage, implementation effort, and compensating controls. A path with one easy-to-fix choke point should not receive the same treatment as a path that requires a long-term architecture change. Both may be serious, but the response plan should reflect the difference.
Remediation ownership also matters. Identity, infrastructure, cloud, application, and business teams often control different portions of the same path. Assigning each finding to a separate team can leave the chain intact. A single accountable risk owner should track whether the complete route has been broken and retested.
Make Attack Path Analysis a Repeatable Practice
Attack paths change whenever the environment changes. New applications, mergers, cloud migrations, identity integrations, vendor connections, and infrastructure-as-code deployments can introduce relationships that did not exist during the prior assessment. A yearly test alone may not keep pace with that change.
Organizations should use attack path analysis at decision points: before major production releases, after identity architecture changes, following an acquisition, when high-impact vulnerabilities emerge, and after a material security incident. Continuous exposure analysis can help identify candidate paths between formal tests, while targeted penetration testing provides the human validation needed to separate theoretical risk from demonstrable compromise.
CyberX approaches this work as an adversary-focused exercise tied to practical decisions. The objective is not to produce a dramatic attack narrative for its own sake. It is to show where defenses fail in sequence, what evidence supports that conclusion, and which actions materially reduce the chance of a successful intrusion.
Questions Leaders Should Ask After Testing
A useful report should answer more than whether testers gained access. Leaders should be able to determine which starting condition was assumed, which controls failed or were bypassed, which control prevented further progress, and whether the evidence would support rapid investigation during a real incident.
They should also ask whether the same path could be repeated by a less capable attacker. A complex chain requiring rare expertise may warrant a different response than a path based on common phishing, reused credentials, and broadly available tools. Neither should be ignored, but risk communication must remain honest about likelihood as well as impact.
The strongest result from attack path analysis is a prioritized plan that security teams can execute, validate, and measure. When the next change introduces a new connection or privilege, revisit the route before an adversary does.